Private by default
Private storage, verified accounts and workspace boundaries help you control access to your business files. Here is exactly how it works, and what it does not do.
Learn more →
Files are held in a private storage bucket with public access disabled. Nothing gets out without an authorised request or a link you chose to create.
Get started free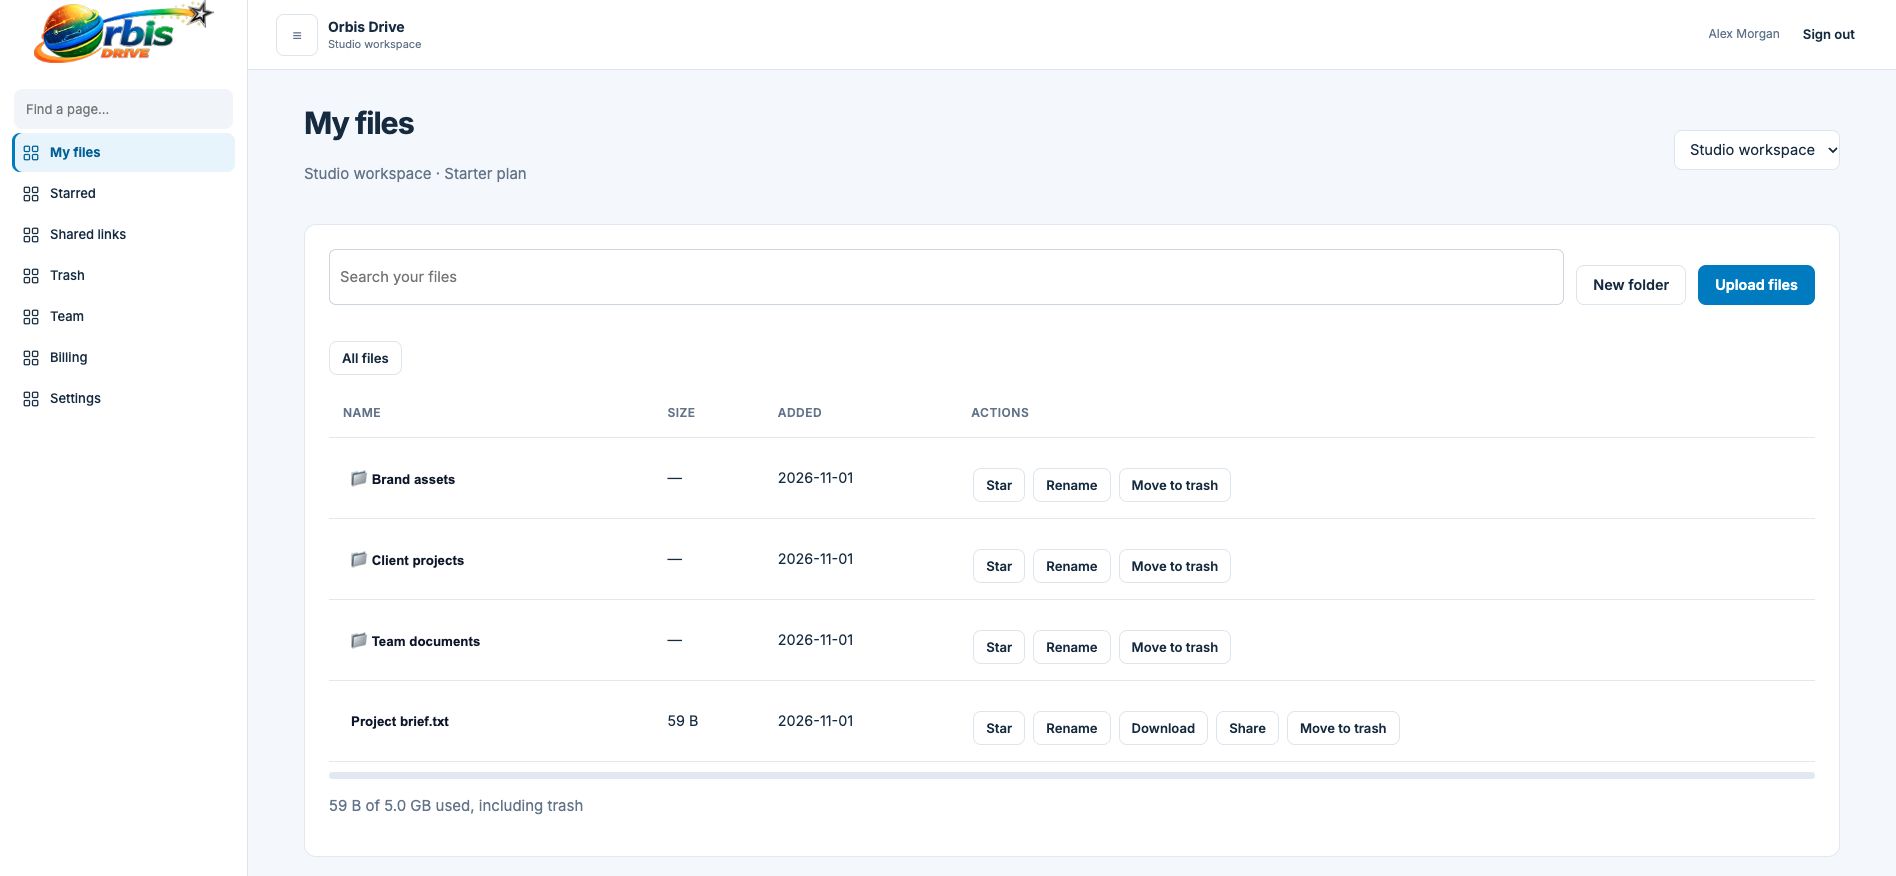
Many data leaks come from storage someone accidentally left open. Orbis Drive keeps every file in a private bucket with no public access, and files are reached only through short-lived addresses issued after a permission check.
Your browser uploads over an encrypted connection using a short-lived, single-purpose address.
Every file is tied to its workspace, and requests are checked against that workspace on each access.
A temporary link lasting 15 minutes is created only after your access has been confirmed.
Files are stored with Cloudflare R2 and application data on our own managed server. Our Privacy Policy lists our suppliers and explains how international transfers are handled.
We do not browse customer content. Because the service is not end-to-end encrypted, it is technically possible for an administrator to access stored data, which is why access is tightly limited and only used where needed to run the service, help you at your request, or meet a legal duty.
Yes. Database, application and stored objects are backed up nightly to encrypted offsite storage. Backups support disaster recovery and are not a way to restore a single file on request.
Private storage, verified accounts and workspace boundaries help you control access to your business files. Here is exactly how it works, and what it does not do.
Learn more →Email addresses are confirmed before anyone can upload or join a workspace, and sign-in is protected with hashed passwords and attempt limits.
Learn more →Key actions such as uploads, deletions, sharing, membership changes and billing events are recorded with the time and the account responsible.
Learn more →